
Certified VAPT Testing & Security Services in Bangalore
We simulate sophisticated cyberattacks to identify vulnerabilities across web applications, mobile apps, APIs, and cloud infrastructure. Protect sensitive enterprise data and achieve SOC 2, ISO 27001, and RBI regulatory compliance.
Complete VAPT & Security Capabilities
Rigorous offensive security assessments safeguarding your digital assets from real-world threats.
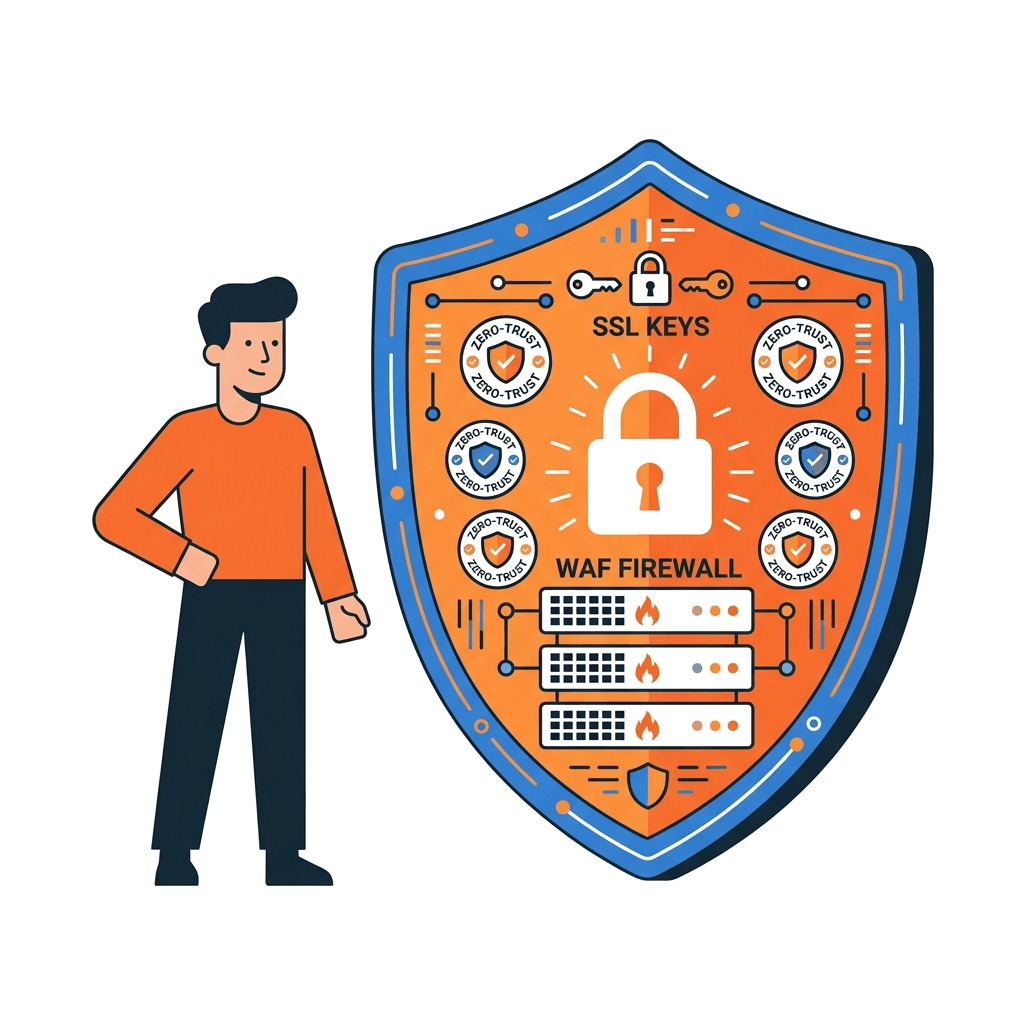
Web Application Penetration Testing
Thorough black-box, grey-box, and white-box pentesting covering SQLi, XSS, CSRF, IDOR, SSRF, and business logic bypasses.
Explore Web Application Penetration Testing
Mobile Application Security (iOS & Android)
Static and dynamic analysis (SAST/DAST) assessing reverse engineering, insecure local storage, root/jailbreak bypass, and SSL pinning.
Explore Mobile Application Security (iOS & Android)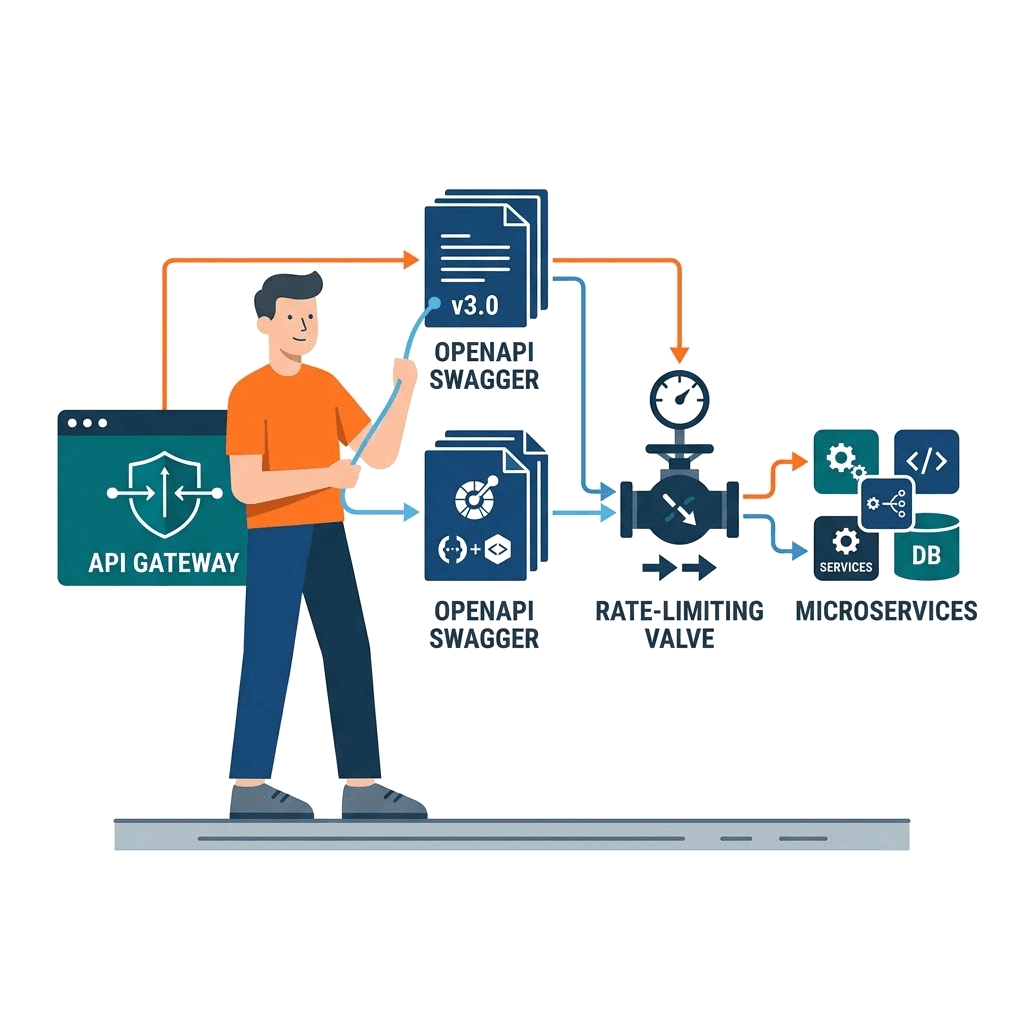
API & Microservices Security Auditing
Testing REST and GraphQL endpoints against OWASP API Security Top 10: broken object-level authorization, mass assignment, and JWT flaws.
Explore API & Microservices Security Auditing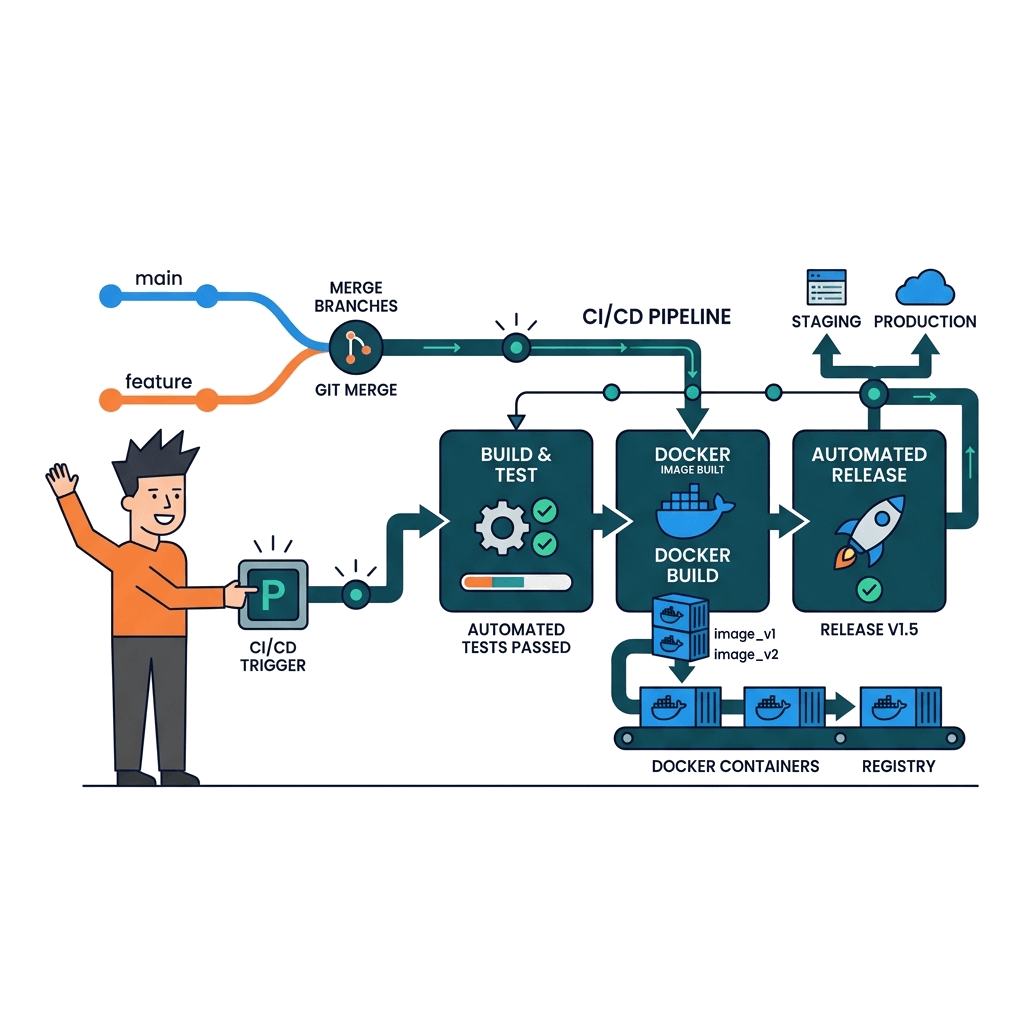
Cloud Infrastructure & Network VAPT
Auditing AWS, Azure, and GCP configurations, open ports, IAM over-privileging, exposed S3 buckets, and Kubernetes security controls.
Explore Cloud Infrastructure & Network VAPT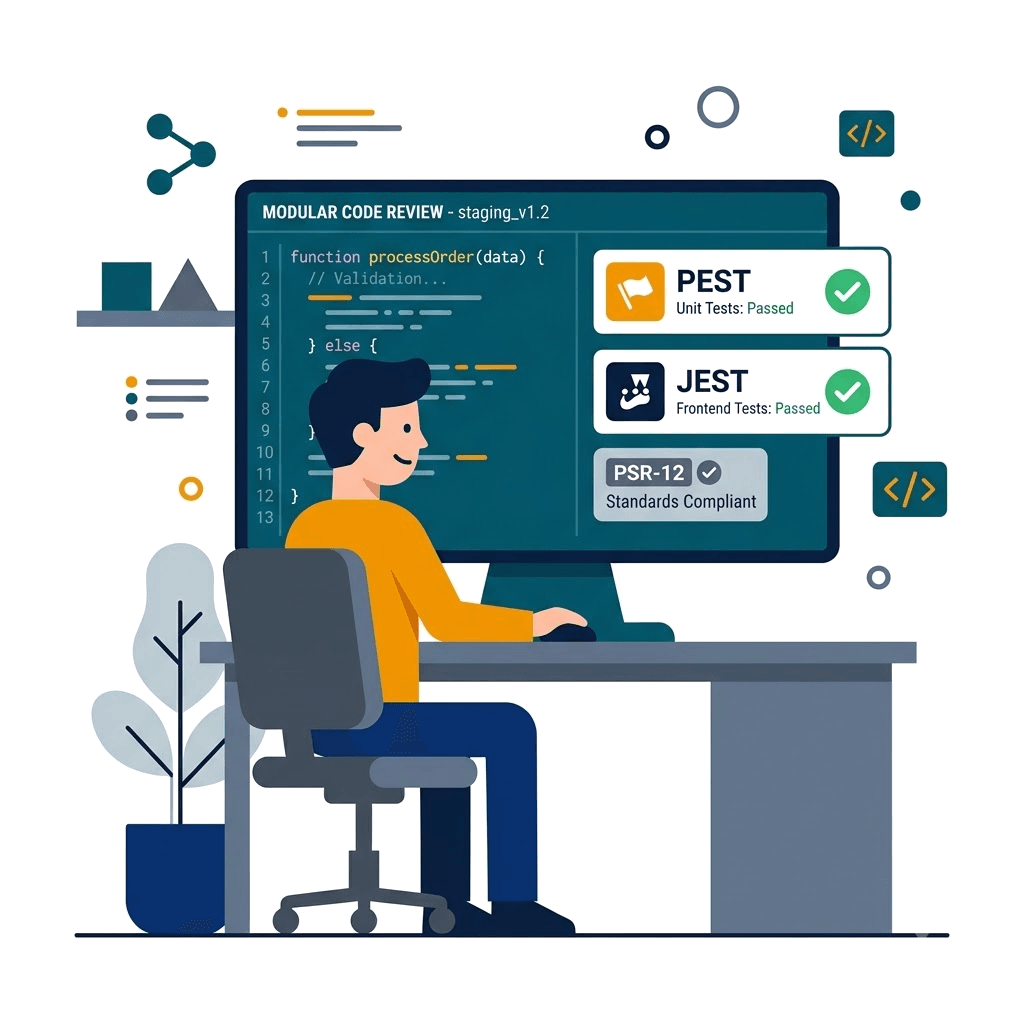
Source Code Security Review (SAST)
Deep automated and manual code audits identifying hardcoded credentials, cryptographic weaknesses, and dependency vulnerabilities.
Explore Source Code Security Review (SAST)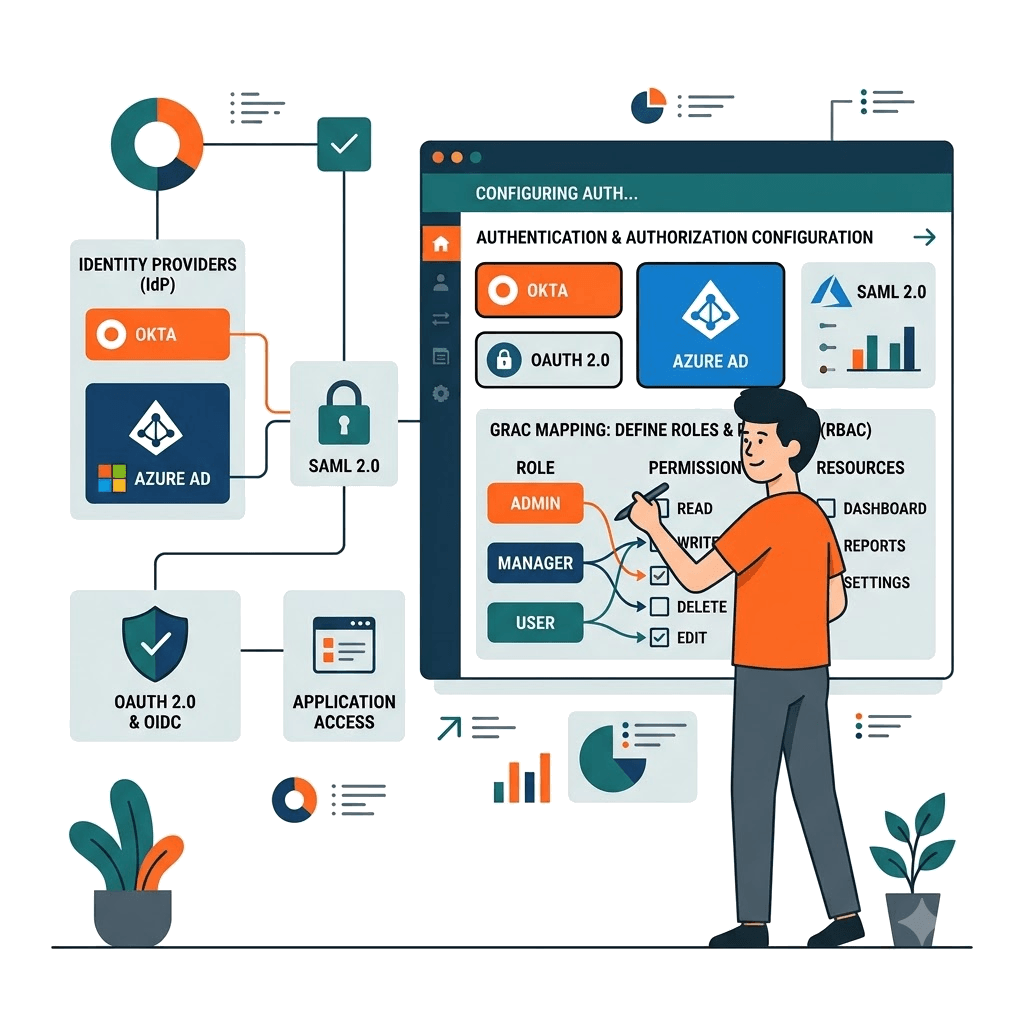
Regulatory Compliance & Certification
Delivering auditor-grade VAPT reports with executive summaries, CVSS 3.1 scores, and retesting verification certificates for compliance.
Explore Regulatory Compliance & CertificationOur Security & Penetration Testing Toolset
Industry-standard offensive security tooling and vulnerability scanners.
Offensive Pentesting
Vulnerability Scanning
Code & Container Security
Cloud Security
Our Rigorous VAPT Lifecycle
A systematic 6-phase offensive security audit methodology adhering to OWASP and NIST guidelines.
Scope Definition & Rules of Engagement
Documenting explicit targets, IP whitelists, testing windows, contact escalations, and authorization sign-offs.
Reconnaissance & Asset Discovery
Passive and active gathering of attack surfaces, subdomains, open ports, exposed APIs, and technology stacks.
Vulnerability Assessment (Automated Scans)
Running authenticated and unauthenticated vulnerability scanners across target endpoints and servers.
Exploitation & Penetration Testing
Senior ethical hackers manually testing business logic flaws, privilege escalations, and data exfiltration paths.
Remediation Guidance & Reporting
Delivering detailed reports with proof-of-concept exploits, CVSS scores, and step-by-step developer fixes.
Retesting & Compliance Certification
Re-evaluating discovered vulnerabilities after developer patches and issuing the official VAPT Certificate.
Enterprise Security Benchmarks
Strict security controls protecting client intellectual property and sensitive customer data.
Zero High/Critical Findings
Comprehensive retesting guaranteeing 100% remediation of all High and Critical CVSS vulnerabilities.
Auditor-Accepted VAPT Certificate
Official verification certificate and executive summary accepted by enterprise clients, banks, and auditors.
Strict NDA & Data Confidentiality
Stringent protocols ensuring zero sensitive client data is stored or exposed during penetration testing.
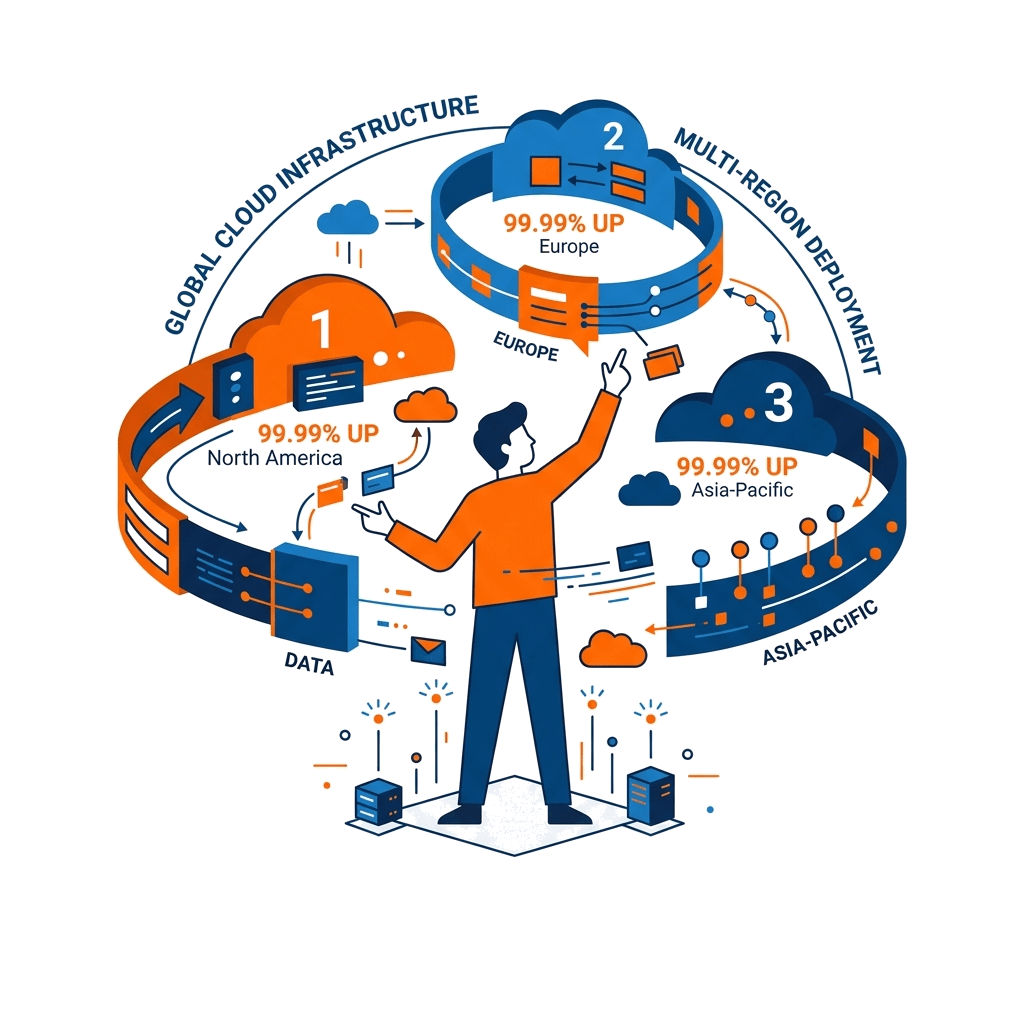
Zero Production Disruption SLA
Carefully calibrated payload limits ensuring mission-critical production systems remain 100% operational.
Actionable Proof of Concept (PoC)
Every finding accompanied by exact reproduction steps and copy-paste remediation code snippets.
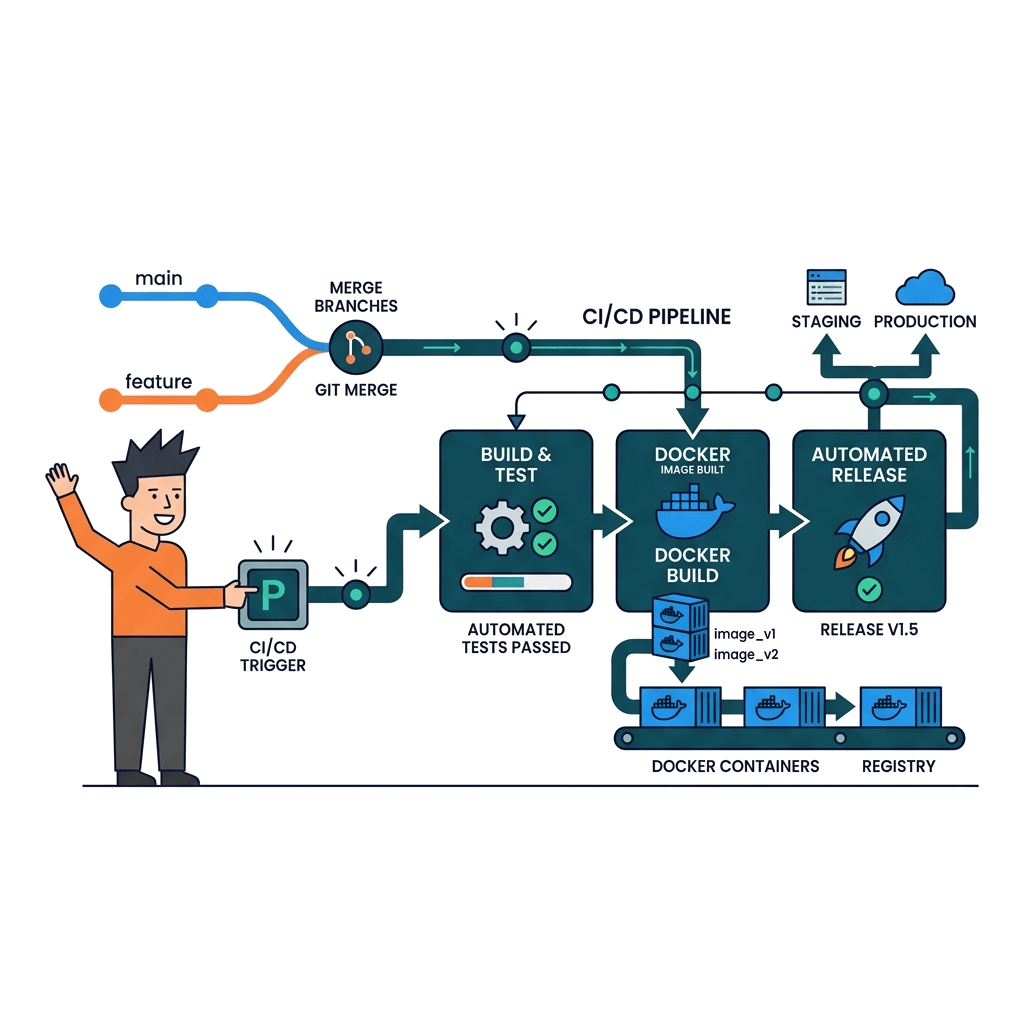
Continuous Security Telemetry
Recommendations for integrating automated security scans into daily developer CI/CD pipelines.
Featured Cybersecurity VAPT Case Study
Comprehensive VAPT and compliance certification for a Series-B fintech startup.
Full-Stack VAPT Audit & SOC 2 Certification for Payment Gateway
Conducted exhaustive web, API, and AWS cloud penetration testing for a high-volume payment processor. Uncovered 3 critical business logic vulnerabilities in authorization token validation, assisted development in patching, and issued compliance certification within 14 days.
Why Partner With Render Infotech?
Over 16+ years and 500+ successful deployments, we have established an engineering reputation in Bangalore for technical rigor, architectural transparency, and zero compromise on code quality.
- Dedicated In-House Engineers: Direct communication with senior specialists, not junior offshore intermediaries.
- 100% IP & Code Ownership: Full source code, database structures, and copyright ownership transferred upon milestone sign-off.
- Performance SLA Guarantee: Contractually committed speed benchmarks, security verification, and high-availability SLAs.
- Transparent Weekly Sprints: Live staging environments, progress demos, and clear milestone accounting.
Enterprise Performance Commitment
Every project we engineer is guaranteed to pass rigorous vulnerability scans, mobile responsiveness checks, and automated regression testing prior to production launch.
Bangalore Engineering Center
Kalyan Nagar, Bengaluru — Local Support & Global Standards
VAPT Testing & Cybersecurity Services FAQs
Answers to common technical, pricing, and timeline questions regarding our VAPT Testing & Cybersecurity Services services.
Ready to Architect Your Solution?
Connect directly with our senior technical architects in Bangalore for an architectural consultation, technology recommendation, and formal scope estimate within 24 hours.
Request a VAPT Testing & Cybersecurity Services Proposal
Fill out your technical brief below to receive an architectural estimate within 24 hours.