
Secure & Optimize: Cloud Security & FinOps Services in Bangalore
We protect cloud infrastructure with automated Zero-Trust security and eliminate runaway cloud waste with disciplined FinOps engineering. Slash your AWS, Azure, and GCP monthly spend by 30% to 50% while achieving SOC 2, ISO 27001, and regulatory compliance.
Complete Cloud Security & FinOps Capabilities
Hardening cloud perimeter security while maximizing every dollar invested in cloud compute.
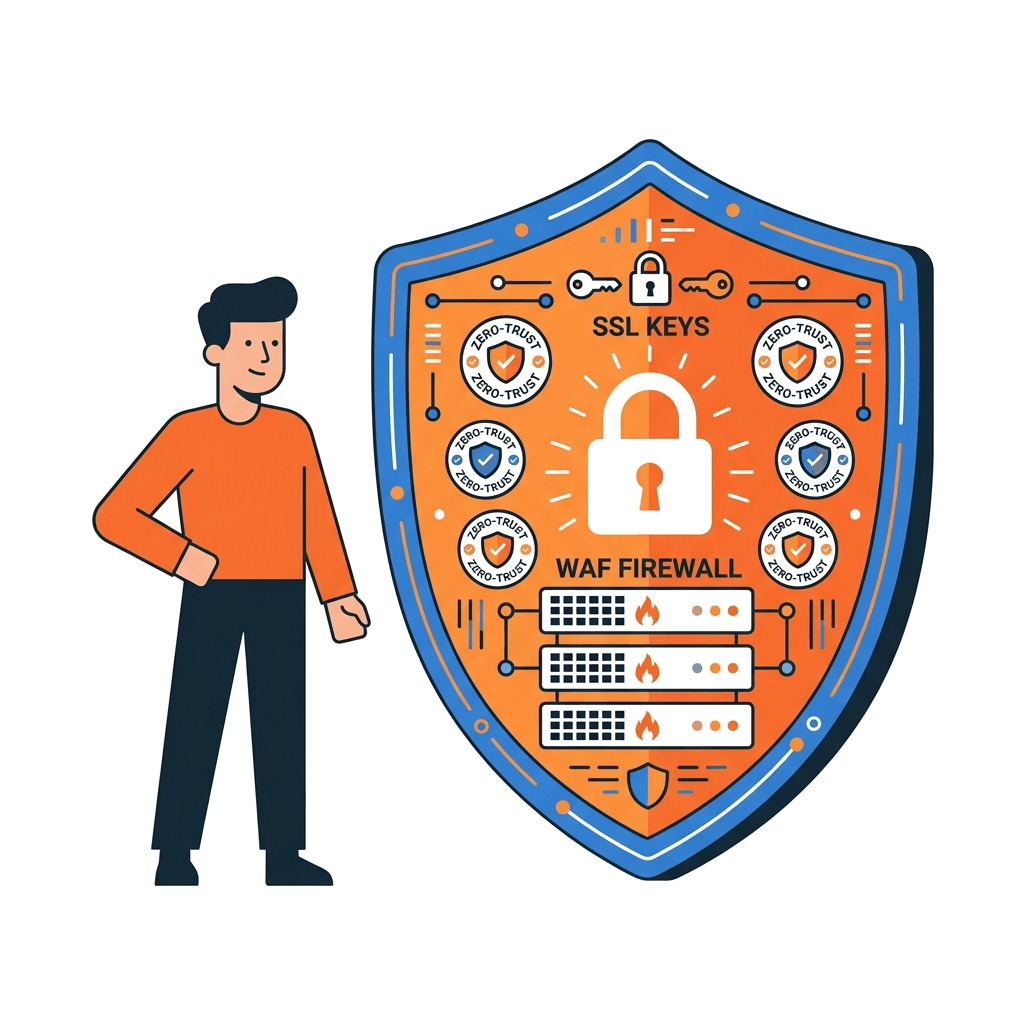
Cloud Security Posture Management (CSPM)
Continuous automated scanning of cloud resources to detect misconfigured S3 buckets, open security groups, and exposed database ports.
Explore Cloud Security Posture Management (CSPM)
FinOps Cloud Cost Optimization & Right-Sizing
Auditing underutilized virtual machines, idle EBS volumes, unattached elastic IPs, and unreserved steady-state compute workloads.
Explore FinOps Cloud Cost Optimization & Right-Sizing
Savings Plans & Reserved Instance Management
Modeling and executing optimal 1-year and 3-year Compute Savings Plans and Reserved Instances to lock in up to 72% hourly discounts.
Explore Savings Plans & Reserved Instance Management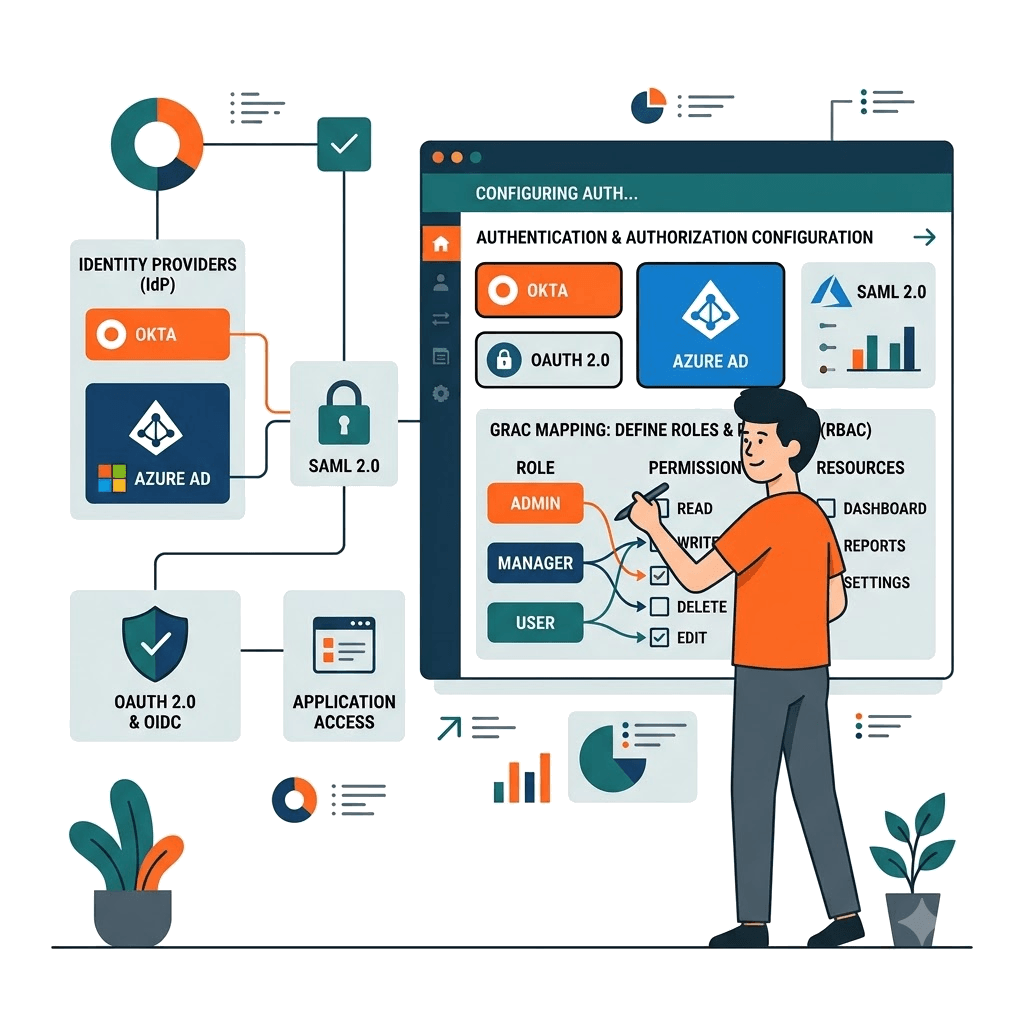
Zero-Trust IAM & Least-Privilege Governance
Auditing over-privileged IAM users, eliminating long-lived access keys, and enforcing automated short-lived role assumption.
Explore Zero-Trust IAM & Least-Privilege Governance
Compliance Hardening (SOC 2, ISO 27001, HIPAA)
Automating cloud evidence collection, KMS encryption key rotation, and audit logs required by regulatory compliance frameworks.
Explore Compliance Hardening (SOC 2, ISO 27001, HIPAA)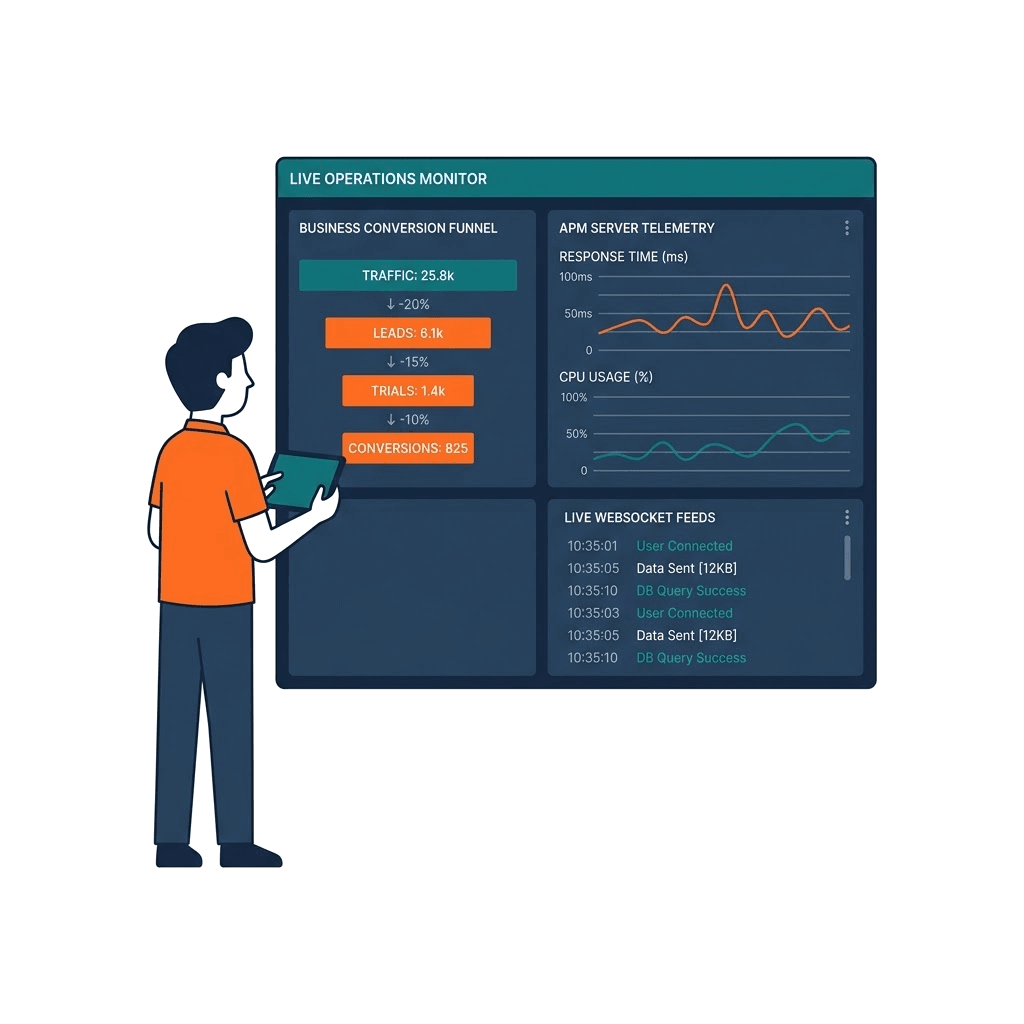
Real-Time Cloud Spend Anomaly Alerting
Implementing automated Slack and email alerts that flag unexpected cloud billing spikes within hours before invoices balloon.
Explore Real-Time Cloud Spend Anomaly AlertingOur Security & FinOps Toolset
Industry-standard CSPM platforms, FinOps analytics tools, and compliance frameworks.
FinOps Platforms
CSPM & Cloud Security
IAM & Identity Security
Compliance & Auditing
Our Security & FinOps Lifecycle
A systematic 6-step roadmap delivering rapid cost reduction and hardened cloud security.
Deep Invoice & Security Baseline Audit
Analyzing 12 months of cloud billing line items and running automated CSPM scans across all cloud accounts.
Quick-Win Cost Waste Elimination
Immediately terminating zombie instances, unattached EBS storage, idle load balancers, and old snapshots.
Workload Right-Sizing & Modernization
Right-sizing over-provisioned VMs and migrating eligible workloads to ARM Graviton processors for 40% savings.
Commitment Modeling (Savings Plans / RIs)
Purchasing flexible 1-year and 3-year Compute Savings Plans covering stable baseline infrastructure.
Zero-Trust Security & IAM Hardening
Closing public security group rules, rotating stale API credentials, and enabling encryption everywhere.
Continuous FinOps Culture & Guardrails
Implementing showback/chargeback tagging policies, Slack cost alerts, and weekly unit-cost tracking.
Enterprise Security & FinOps Standards
Guaranteed cost reductions, hardened cloud perimeter, and zero security drift.
Minimum 30% Cost Reduction SLA
Guaranteeing measurable cloud bill reductions through structured waste elimination and right-sizing.
Zero Exposed Production Storage
Strict policies ensuring zero S3 buckets or database snapshots have public read or write access.
100% Resource Allocation Tagging
Enforcing cost-center and environment tags on all resources to enable accurate departmental showback.
Automated Spend Anomaly Paging
Alerting within 2 hours if any individual cloud service expenditure deviates by more than 20% from baseline.
Zero Hardcoded IAM Access Keys
Enforcing IAM roles, instance profiles, and temporary STS credentials across all applications.
Auditor-Ready SOC 2 Evidence
Automated compliance evidence collection ensuring seamless certification audits.
Featured Security & FinOps Case Study
Cutting monthly AWS cloud expenditure by 47% while passing a SOC 2 Type II audit.
AWS FinOps Optimization & SOC 2 Compliance for SaaS Platform
Audited an over-provisioned AWS environment for a B2B SaaS platform. Terminated 45 unattached EBS volumes, converted EC2 workloads to Graviton3 instances with 3-year Compute Savings Plans, and remediated 32 security misconfigurations to achieve SOC 2 Type II certification.
Why Partner With Render Infotech?
Over 16+ years and 500+ successful deployments, we have established an engineering reputation in Bangalore for technical rigor, architectural transparency, and zero compromise on code quality.
- Dedicated In-House Engineers: Direct communication with senior specialists, not junior offshore intermediaries.
- 100% IP & Code Ownership: Full source code, database structures, and copyright ownership transferred upon milestone sign-off.
- Performance SLA Guarantee: Contractually committed speed benchmarks, security verification, and high-availability SLAs.
- Transparent Weekly Sprints: Live staging environments, progress demos, and clear milestone accounting.
Enterprise Performance Commitment
Every project we engineer is guaranteed to pass rigorous vulnerability scans, mobile responsiveness checks, and automated regression testing prior to production launch.
Bangalore Engineering Center
Kalyan Nagar, Bengaluru — Local Support & Global Standards
Cloud Security & FinOps Services FAQs
Answers to common technical, pricing, and timeline questions regarding our Cloud Security & FinOps Services services.
Ready to Architect Your Solution?
Connect directly with our senior technical architects in Bangalore for an architectural consultation, technology recommendation, and formal scope estimate within 24 hours.
Request a Cloud Security & FinOps Services Proposal
Fill out your technical brief below to receive an architectural estimate within 24 hours.